
Breaking into cybersecurity creates a frustrating problem: many entry-level jobs ask for experience, but you need a job to gain that experience. Cybersecurity internships help bridge that gap by letting students, recent graduates, and career changers apply security knowledge in a supervised professional environment.
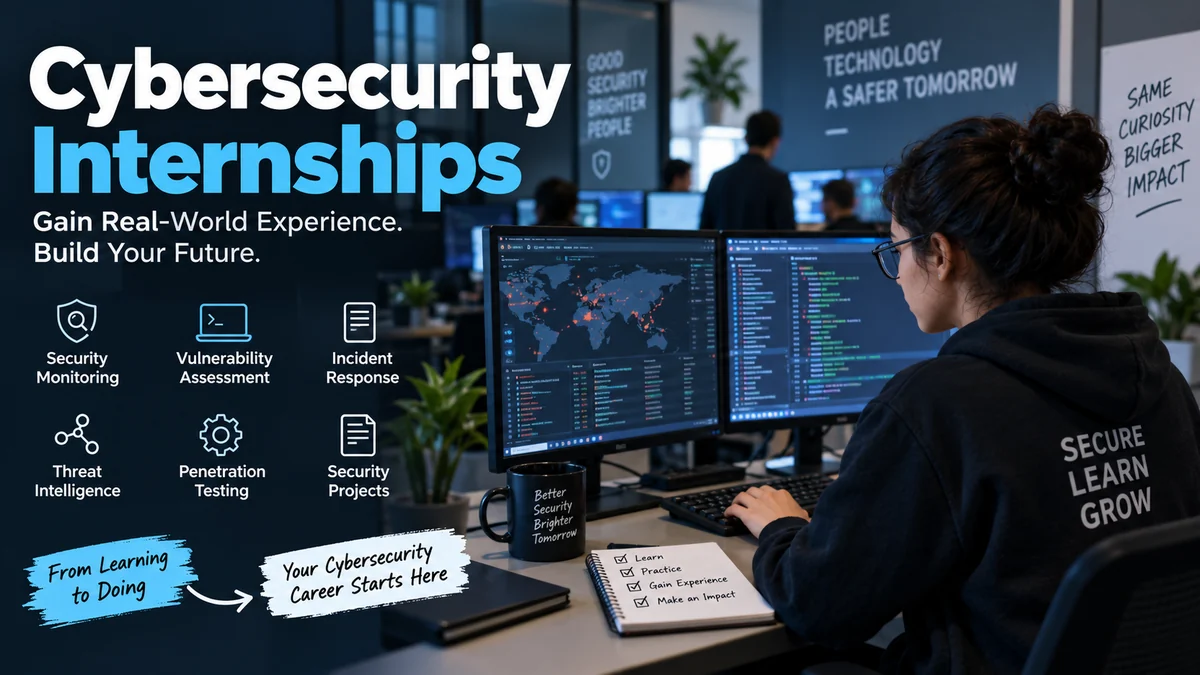
Cybersecurity internships are temporary positions where interns gain hands-on experience protecting systems, networks, applications, and data. Typical work includes security monitoring, vulnerability assessment, incident response, threat intelligence, penetration testing, digital forensics, compliance, and scripting. Internships may be paid, unpaid, remote, on-site, summer-based, or completed for academic credit.
The work can be far more practical than classroom study. Instead of only learning what a vulnerability is, you might investigate one, document its risk, recommend remediation, and explain the result to a security team.
What Do Cybersecurity Interns Actually Do?
There is no single job description for a cybersecurity intern. Responsibilities depend heavily on the employer, industry, security team, and internship track.
Current internship guides and programs commonly describe work involving security-event monitoring, vulnerability assessments, web application security, threat research, incident response, penetration testing, scripting, and security projects.
An intern working in a Security Operations Center (SOC), for example, may spend time reviewing alerts and investigating suspicious activity. Someone on an application security team could test web applications and help developers understand vulnerabilities.
Typical responsibilities include:
- Reviewing security alerts and logs
- Investigating suspicious network or endpoint activity
- Performing vulnerability scans
- Researching emerging threats
- Assisting with incident response
- Testing web application security
- Helping with penetration tests
- Documenting vulnerabilities and remediation steps
- Writing Python, Bash, or PowerShell scripts
- Supporting security audits
- Reviewing security policies
- Preparing technical reports
- Performing digital forensics exercises
- Improving security awareness materials
Interns normally work under experienced analysts, engineers, consultants, or security managers rather than independently handling high-risk incidents.
Some organizations assign interns a specific project instead. That could involve building a small detection system, creating an automation script, reviewing security controls, conducting an authorized assessment, or researching a particular threat.
Quick Takeaway: A useful internship should give you evidence that you can apply cybersecurity concepts, not simply give you a cybersecurity-related job title.
Types of Cybersecurity Internships
Cybersecurity is a collection of specialties rather than one occupation. Understanding these areas makes searching much easier.
Security Operations Center Internships
SOC internships are among the most recognizable entry points.
You may work with:
- Security Information and Event Management (SIEM) platforms
- Endpoint security systems
- Network logs
- Security alerts
- Indicators of compromise
- Incident tickets
The work develops skills relevant to future SOC analyst and security analyst positions.
Networking fundamentals matter here. You should understand IP addresses, DNS, HTTP/HTTPS, TCP/IP, ports, authentication, and common network protocols.
Incident Response and Threat Intelligence
Incident response interns help security teams investigate potential compromises.
Tasks can include analyzing logs, building timelines, collecting evidence, researching indicators of compromise, documenting incidents, and studying attacker behavior.
Threat intelligence work adds research. You might examine phishing campaigns, malware families, attacker infrastructure, vulnerabilities, or tactics used by threat actors.
Vulnerability Assessment and Penetration Testing
These internships focus on finding weaknesses before attackers exploit them.
You might learn about:
- Vulnerability scanning
- Network reconnaissance
- Web application testing
- Security misconfigurations
- Risk prioritization
- Penetration testing
- Remediation validation
Tools can include Nmap, Burp Suite, Wireshark and vulnerability scanners, depending on the organization’s environment and authorization.
Penetration testing should always take place within an explicitly authorized scope.
Application Security
Application security, often shortened to AppSec, combines cybersecurity with software development.
Interns may review applications for weaknesses, perform security testing, examine code, reproduce vulnerabilities, or help integrate security checks into the software development lifecycle.
Knowledge of the OWASP Top 10 can provide a useful foundation for web security.
Digital Forensics
Digital forensics focuses on collecting and analyzing digital evidence.
An internship may introduce you to file systems, disk images, event logs, memory analysis, metadata, evidence handling, and forensic investigation methods.
It can be particularly relevant for students interested in DFIR—digital forensics and incident response.
Governance, Risk, and Compliance
Not every cybersecurity internship involves hacking or command-line tools.
Governance, Risk, and Compliance (GRC) teams examine organizational security requirements, risks, policies, controls, audits, and regulatory obligations.
Interns might:
- Review security policies
- Map controls to frameworks
- Assist with risk assessments
- Gather audit evidence
- Maintain compliance documentation
- Review third-party security information
Frameworks and standards such as the NIST Cybersecurity Framework and ISO/IEC 27001 frequently appear in this area.
Cloud Security
Cloud security internships can expose students to environments built on services from providers such as Amazon Web Services, Microsoft Azure, and Google Cloud.
Relevant concepts include Identity and Access Management (IAM), least privilege, cloud logging, storage permissions, network controls, encryption, secrets management, and configuration monitoring.
Security Engineering and Automation
Students with stronger programming backgrounds may find internships involving security engineering, DevSecOps, detection engineering, or automation.
Python is particularly useful, while Bash and PowerShell can help with Linux and Windows administration.
The objective is not necessarily to become a professional software developer. Even small scripts that parse logs, query APIs, process indicators, or automate repetitive work can demonstrate valuable problem-solving ability.
What Skills Do You Need for Cybersecurity Internships?
You do not need to know everything before applying.
Employers understand that an intern is still learning. However, “no professional experience required” does not necessarily mean “no technical knowledge required.” Current internship guidance commonly emphasizes networking, operating systems, security fundamentals, programming or scripting, communication, and demonstrable practical work.
Networking Fundamentals
Learn how computers communicate.
Be comfortable explaining:
- IP addresses
- Subnets
- TCP and UDP
- DNS
- DHCP
- HTTP and HTTPS
- Common ports
- Firewalls
- VPNs
- Routers and switches
You do not have to become a network engineer, but networking knowledge makes security alerts and attacks considerably easier to understand.
Windows and Linux
Cybersecurity professionals regularly investigate operating systems.
Learn basic Linux commands, permissions, processes, services, package management, logs, SSH, and file systems.
For Windows, understand users and groups, processes, services, permissions, PowerShell, Windows Event Logs, and basic Active Directory concepts.
Security Fundamentals
Before chasing advanced offensive techniques, understand basic concepts such as:
- Confidentiality, integrity, and availability
- Authentication and authorization
- Least privilege
- Encryption
- Hashing
- Vulnerabilities
- Malware
- Phishing
- Access control
- Network segmentation
- Security monitoring
- Incident response
Strong fundamentals usually make unfamiliar security tools easier to learn.
Programming and Scripting
Programming requirements vary considerably between roles.
Python is useful because it can automate repetitive tasks, interact with APIs, manipulate files, and process security data. Bash is valuable in Linux environments, while PowerShell is highly relevant to Windows.
Pakistan’s National CERT, for example, identifies Python, Java, C/C++, Bash, PowerShell, database knowledge, networking, operating systems, security frameworks, incident response, vulnerability assessment, and threat intelligence among useful internship competencies.
Communication
Technical ability alone is not enough.
An intern may need to explain:
- What happened
- Why it matters
- What evidence supports the finding
- How serious the risk is
- What should happen next
Clear technical writing is particularly valuable because cybersecurity produces reports, tickets, incident notes, procedures, and risk assessments.
Can You Get a Cybersecurity Internship With No Experience?
Yes, because internships are specifically designed to provide experience. The more useful distinction is between having no employment experience and having no evidence of cybersecurity ability.
You can create that evidence yourself.
A candidate without professional experience can still show:
- Home lab projects
- Capture the Flag (CTF) exercises
- GitHub projects
- Security research
- Networking labs
- Vulnerability assessment reports
- Programming projects
- University projects
- Hackathons
- Bug bounty participation
- Open-source contributions
Competitor guidance increasingly emphasizes demonstrable projects and portfolios alongside academic credentials and certifications.
Build a Small Home Lab
A basic lab can include virtual machines running Linux and Windows.
You could practice:
- Configuring the machines.
- Creating users and permissions.
- Capturing traffic with Wireshark.
- Examining operating-system logs.
- Running authorized vulnerability scans against your own systems.
- Hardening insecure configurations.
- Documenting what changed.
Documentation is what transforms experimentation into portfolio evidence.
Instead of writing “Used Wireshark,” explain what you investigated, how you analyzed the traffic, what you found, and what conclusion you reached.
Complete a Few Focused Projects
Three well-documented projects can be more useful than dozens of unfinished tutorials.
For example:
Project 1: Network Traffic Analysis
Capture traffic in a controlled lab, analyze DNS and HTTP requests, identify notable patterns, and write a short investigation report.
Project 2: Vulnerability Assessment
Scan an intentionally vulnerable lab environment, categorize the findings, research remediation, fix selected issues, and verify the changes.
Project 3: Security Log Investigation
Generate sample authentication activity, review the logs, identify failed-login patterns, and create a simple Python script that summarizes suspicious attempts.
These projects demonstrate technical knowledge, investigation, communication, and problem solving at the same time.
Do You Need a Cybersecurity Degree?
Not for every internship.
Many programs target students enrolled in cybersecurity, information security, computer science, information technology, engineering, or related programs. Others consider self-taught candidates, career changers, or recent graduates.
Government programs may impose stricter requirements involving enrollment, citizenship, academic status, or security clearance.
For example, Pakistan’s 2026 Higher Education Commission draft BS Cyber Security curriculum specifies field experience or an internship as a mandatory component of the degree, carrying three credit hours and requiring at least 150 working hours. It allows on-site, remote, and approved project/workshop formats subject to university requirements.
Always read the eligibility section before applying rather than assuming every cybersecurity internship follows the same rules.
Do Certifications Help?
Certifications can strengthen an application, but they should not replace practical evidence.
Entry-level candidates commonly investigate credentials such as CompTIA Security+ or other introductory security, networking, cloud, or vendor certifications.
A certification can demonstrate structured learning. It cannot by itself show how you investigate a problem.
A stronger profile might therefore combine:
security fundamentals + certification + home lab + documented projects + communication skills.
Avoid collecting certifications simply because they appear on job descriptions. First determine which cybersecurity path interests you and which credential supports it.
How to Build a Cybersecurity Internship Resume
A student resume should not imitate the resume of someone with five years of professional security experience.
If your employment history is limited, make relevant evidence easy to find.
A practical structure is:
- Contact information
- Short professional summary
- Technical skills
- Cybersecurity projects
- Education
- Certifications
- Relevant experience
- Activities, competitions, or volunteer work
Current career guidance recommends emphasizing coursework, IT experience, transferable skills, technical projects, competitions, and other evidence when direct professional cybersecurity experience is unavailable.
Write Projects Like Real Experience
Weak:
Cybersecurity home lab using Linux.
Better:
Built an isolated Linux security lab, captured and analyzed network traffic with Wireshark, reviewed authentication logs, and documented suspicious login patterns and remediation steps.
The second version explains what you actually did.
Use measurable results where they genuinely exist, but never invent numbers.
Tailor Your Resume
A SOC internship and GRC internship should not receive identical resumes.
For a SOC position, emphasize networking, SIEM exposure, logs, incident investigation, Linux, and threat analysis.
For GRC, prioritize frameworks, risk assessment, documentation, policies, auditing, and communication.
For AppSec, highlight programming, Git, web technologies, OWASP concepts, security testing, and development projects.
How to Find Cybersecurity Internships
Searching only for the exact phrase cybersecurity internships can cause you to miss relevant positions.
Employers use many different titles.
Try searches such as:
- Cybersecurity intern
- Information security intern
- SOC intern
- Security analyst intern
- Information security analyst intern
- Cyber defense intern
- GRC intern
- Security engineering intern
- Application security intern
- Cloud security intern
- Threat intelligence intern
- Incident response intern
- Digital forensics intern
- Vulnerability management intern
Major job platforms, university career portals, government programs, professional networks, and employers’ own career pages can all surface opportunities.
LinkedIn and Indeed are common general-purpose sources, while university career services and government portals can reveal programs that broad job searches miss.
Look Beyond Technology Companies
Cybersecurity exists anywhere valuable data and systems exist.
That means internships can appear at:
- Banks
- Hospitals
- Universities
- Government agencies
- Telecommunications companies
- Consulting firms
- Defense organizations
- Software companies
- Manufacturers
- Retailers
- Managed security service providers
- Cybersecurity vendors
Searching by security function instead of simply searching for “cybersecurity company” expands your options.
Government Cybersecurity Internships
Government agencies often operate structured student programs because protecting public infrastructure and information requires a continuing security workforce.
In the United States, organizations including the Cybersecurity and Infrastructure Security Agency (CISA), Department of Homeland Security (DHS), and National Security Agency (NSA) operate student or early-career programs, although eligibility and availability differ by program.
Government security positions may involve citizenship, background investigations, security clearance requirements, or longer application timelines.
Cybersecurity Internships in Pakistan
Pakistan also provides government-backed opportunities.
The National Cyber Emergency Response Team (National CERT/PKCERT) ran a 2026 summer internship program designed around hands-on training, mentorship, practical challenges, and real-world cybersecurity exposure. Its listed domains included Governance, Compliance & Audit; Incident Management & Threat Intelligence; Vulnerability Assessment & Pen Testing; Software Security Testing; Digital Forensics; AI & Software Development; and Hardware Screening, among other areas.
The published 2026 application window has already closed, so students researching future opportunities should use the official program information to understand the skills and eligibility requirements rather than treating old application dates as current openings.
That distinction matters whenever you find internship articles through Google: always confirm deadlines on the organization’s official website.
Remote vs. On-Site Cybersecurity Internships
Remote internships provide flexibility and allow students to apply outside their immediate area.
They can also require more independence.
| Factor | Remote Internship | On-Site Internship |
|---|---|---|
| Location | Flexible | Fixed workplace |
| Communication | Mostly digital | Direct interaction |
| Mentoring | Scheduled/virtual | Often easier informally |
| Independence | Usually higher | Varies |
| Networking | Requires deliberate effort | More natural interaction |
| Lab access | May be restricted | Often easier |
| Commute | None | Usually required |
Neither format is automatically better.
A well-structured remote program with regular mentorship, meaningful projects, and feedback can be far more educational than an on-site internship consisting mostly of administrative work.
Evaluate the work, supervision, learning opportunities, and expected deliverables rather than the location alone.
When Should You Apply?
Do not wait until summer begins to search for a summer internship.
Large employers and government organizations may recruit months in advance. Smaller companies and startups can operate on shorter schedules.
A sensible strategy is to start researching employers several months before your preferred start date and apply as opportunities open. Some current 2026 internship guidance recommends beginning roughly three to five months ahead, while certain large programs recruit considerably earlier.
Create a simple application tracker containing:
| Field | What to Record |
|---|---|
| Company | Employer name |
| Position | Exact internship title |
| Track | SOC, GRC, AppSec, etc. |
| Location | Remote/hybrid/on-site |
| Deadline | Final application date |
| Applied | Date submitted |
| Contact | Recruiter or referral |
| Status | Applied/interview/rejected/offer |
| Follow-up | Next action |
This prevents missed deadlines and duplicate applications.
How to Prepare for a Cybersecurity Internship Interview
Technical interviews for interns usually test fundamentals more than obscure expert-level knowledge.
Be prepared to explain concepts rather than recite definitions.
You could be asked:
What happens when you type a website address into a browser?
A good response connects DNS resolution, networking, TCP/TLS where applicable, HTTP requests, servers, and responses.
What is the difference between hashing and encryption?
Explain that encryption is designed to be reversible with the appropriate key, while cryptographic hashing produces a fixed representation designed to be one-way.
What would you do if you noticed suspicious login activity?
Walk through validation, evidence collection, scope assessment, escalation, containment considerations, documentation, and adherence to organizational procedures.
What is least privilege?
Explain why users and systems should receive only the permissions necessary for their responsibilities.
Expect Questions About Your Projects
If your resume says you built a lab, interviewers may ask:
- Why did you build it?
- How was the network configured?
- What went wrong?
- What did you investigate?
- Which tools did you use?
- What did you learn?
- What would you change next time?
Never add a tool to your resume merely because you followed one tutorial with it.
Understanding three tools well is more defensible than listing twenty that you cannot explain.
Common Mistakes That Hurt Internship Applications
Applying Only to Famous Companies
Well-known technology and cybersecurity firms attract enormous applicant pools.
Apply there, but also investigate banks, universities, hospitals, consulting firms, local businesses, government organizations, and security service providers.
Collecting Certificates Without Building Anything
Learning is useful. Evidence of applying that learning is better.
Turn courses into projects whenever possible.
Copying the Same Resume Everywhere
Security roles have different priorities.
Match your strongest relevant evidence to the internship description.
Ignoring Soft Skills
Cybersecurity is collaborative work.
Analysts communicate with engineers, managers, developers, customers, auditors, and employees. Technical findings have little value if nobody can understand them.
Trying to Look Like an Expert
Internships exist for people who are learning.
Being able to say “I haven’t worked with that yet, but here is how I would approach learning it” can be more credible than bluffing.
Failing to Document Projects
A project that exists only on your laptop is difficult for a recruiter to evaluate.
Create sanitized documentation, diagrams, screenshots, scripts, or GitHub repositories when appropriate. Never publish confidential information, credentials, unauthorized data, or exploit details that could create unnecessary risk.
How to Make the Most of Your Internship
Getting accepted is only the beginning.
Keep notes about technologies, projects, processes, and lessons learned. Ask thoughtful questions after doing enough research to understand the problem.
Seek feedback regularly rather than waiting until the final week.
Build professional relationships with analysts, engineers, managers, and fellow interns.
Most importantly, understand why security teams perform particular actions.
If you investigate an alert, don’t stop at learning which buttons to click in a SIEM. Understand what generated the event, why the activity was suspicious, what evidence supported the decision, and what response followed.
At the end of the internship, document achievements you are permitted to disclose.
For example:
Investigated endpoint and authentication alerts under analyst supervision and documented findings using the organization’s incident-management workflow.
That becomes useful material for future resumes and interviews.
A Practical Roadmap From Beginner to Internship Applicant
If you are starting from zero, avoid trying to learn every cybersecurity specialty simultaneously.
Use a structured sequence.
Step 1: Learn IT and Networking Fundamentals
Understand computers, operating systems, TCP/IP, DNS, HTTP, common ports, basic troubleshooting, and network architecture.
Step 2: Learn Linux and Windows
Practice navigating both operating systems and working with accounts, permissions, processes, services, logs, and command-line tools.
Step 3: Learn Core Security Concepts
Study vulnerabilities, authentication, access control, malware, phishing, cryptography, network defense, security monitoring, risk, and incident response.
Step 4: Choose an Initial Direction
Explore SOC/security operations, penetration testing, GRC, digital forensics, AppSec, cloud security, or security engineering.
You can change direction later.
Step 5: Build Two or Three Projects
Choose projects relevant to the track you want.
Document the objective, environment, methodology, results, problems encountered, and lessons learned.
Step 6: Create Your Resume and Portfolio
Make your strongest practical evidence immediately visible.
GitHub can be useful for scripts, documentation, and technical projects where publishing the material is appropriate.
Step 7: Start Applying Early
Search multiple job titles and employer types instead of waiting for one ideal opportunity.
Step 8: Practice Interviews
Review networking, operating systems, security fundamentals, and every project mentioned on your resume.
Practice explaining technical concepts in simple language.
Step 9: Keep Learning While Applying
Rejection does not automatically mean you need another certification.
Review the positions you are targeting and identify recurring gaps. If ten SOC internship descriptions mention log analysis and you have never analyzed logs, that is a clear learning priority.
Are Cybersecurity Internships Worth It?
For someone trying to enter the field, a strong internship can solve several problems simultaneously.
It can provide:
- Real-world security experience
- Exposure to professional tools
- Mentorship
- Portfolio material
- Professional references
- Industry contacts
- Better understanding of cybersecurity specialties
- Evidence for future entry-level applications
The biggest value is context.
A course can teach incident response as a sequence of stages. An internship can show how an actual organization balances security risk, business operations, incomplete information, escalation procedures, communication, documentation, and time pressure.
That experience makes theoretical knowledge more meaningful.
Cybersecurity internships are therefore best viewed as a bridge between learning security and practicing it professionally. Build strong IT fundamentals, create evidence of hands-on ability, document a few meaningful projects, tailor your applications, and search beyond obvious job titles and famous employers.
You do not need to master cybersecurity before applying. You need enough foundational knowledge to contribute safely, enough practical evidence to demonstrate genuine interest, and enough curiosity to keep learning once you get the opportunity.
